Endpoint security is essential for protecting modern software products against malware, ransomware, unauthorized access, and other cyber threats. However, integrating security features into existing products can create challenges related to system performance, compatibility, and resource consumption. Original equipment manufacturers (OEMs) must ensure that security controls work effectively without slowing applications or disrupting user experiences.
A well-planned OEM endpoint security integration solution helps software vendors incorporate protection into their products while maintaining reliability and efficiency. Achieving this balance requires optimized security components, thorough testing, and continuous monitoring.
Key Takeaways
Optimize security components to minimize unnecessary resource consumption.
Test compatibility and application performance before deployment.
Use risk-based monitoring to prioritize suspicious activity.
Combine endpoint protection with network security and access controls.
Evaluate scalability, maintenance, and technical support before selecting an integration approach.
Why Performance Matters in Endpoint Security Integration
Endpoint security tools monitor devices, applications, files, and processes to identify potential threats. Although these activities improve protection, they can consume CPU, memory, and network resources when poorly configured.
For OEMs, maintaining performance is particularly important because their products may operate across different devices, operating systems, and business environments. Security features should function efficiently without interfering with essential application operations.
The Impact of Security Tools on System Resources
Frequent system scans, continuous monitoring, and redundant security processes can affect application responsiveness. For example, running resource-intensive scans during peak business hours may slow down applications and interrupt employee productivity.
Development teams can reduce these effects by:
Scheduling intensive scans during periods of low activity.
Minimizing duplicate monitoring processes.
Using efficient scanning and detection techniques.
Testing resource consumption under realistic workloads.
These practices help maintain performance while preserving essential security controls.
Maintaining a Smooth User Experience
Users expect applications to remain responsive while security processes operate in the background. Slow startup times, excessive alerts, and unexpected interruptions can reduce productivity and confidence in a product.
OEMs should evaluate how security integration affects application launches, file transfers, authentication, and routine workflows. Comparing performance before and after integration can help identify bottlenecks and guide optimization.
Common Challenges in OEM Endpoint Security Integration
Integrating security capabilities into existing software requires careful planning. Differences in system configurations, application dependencies, and security requirements can introduce technical complications.
Compatibility With Existing Software and Hardware
OEM products may need to support multiple operating systems, hardware configurations, and third-party applications. Security components that work well in one environment may cause conflicts in another.
To minimize compatibility issues, development teams should test supported operating systems, application dependencies, existing security tools, and update procedures. Early testing can help prevent installation failures, application crashes, and unexpected behavior after deployment.
Managing Real-Time Threat Detection
Real-time monitoring helps identify suspicious behavior before it develops into a serious security incident. However, analyzing every event with the same intensity can increase resource consumption.
Risk-based monitoring allows security components to prioritize potentially harmful activities while maintaining essential background protection. Optimization should never create unnecessary blind spots or prevent critical threats from being detected.
Preventing False Positives
False positives occur when legitimate activity is incorrectly identified as malicious. Excessive alerts can interrupt workflows and make it harder for security teams to identify genuine threats.
Regular testing, appropriate policy configuration, and careful management of exceptions can improve detection accuracy. Organizations should investigate recurring false positives instead of disabling important security controls.
Strategies for Balancing Security and Performance
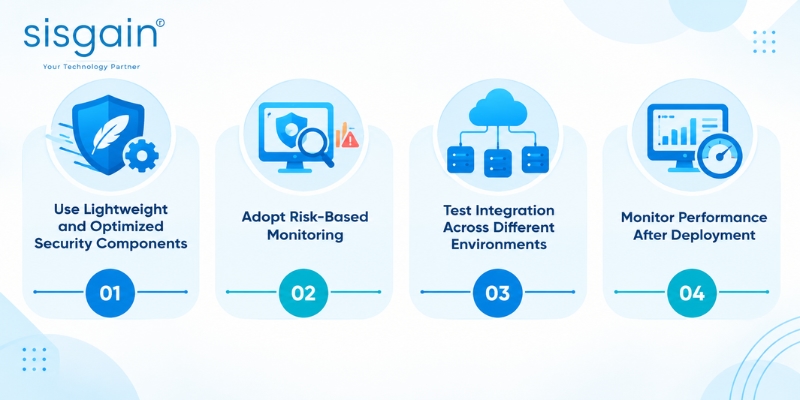
A successful integration strategy combines efficient architecture, realistic testing, and continuous improvement. OEMs should assess both security effectiveness and application performance throughout development.
Use Lightweight and Optimized Security Components
Security components should use system resources efficiently. Modular architecture can help vendors include the capabilities their products require without introducing unnecessary functionality.
Efficient scanning, controlled background processing, and reduced duplication can improve performance. Where appropriate, caching and event-driven monitoring may also reduce repeated processing.
However, optimization must be supported by security testing to ensure that reduced resource consumption does not weaken threat detection.
Adopt Risk-Based Monitoring
Not every system event presents the same level of risk. Risk-based monitoring prioritizes suspicious behavior and allocates resources according to potential impact.
For instance, unexpected privilege escalation or unusual changes to critical files may warrant closer investigation than routine activity from a trusted application.
This approach can improve efficiency while maintaining appropriate protection. Essential monitoring should remain active to ensure that less obvious threats are not overlooked.
Test Integration Across Different Environments
Testing should begin before security components are released to customers. OEMs should evaluate compatibility, stability, and performance across supported hardware, operating systems, and application workloads.
A comprehensive testing process should assess:
Performance: Measure CPU usage, memory consumption, and application response times.
Compatibility: Check interactions with existing applications and security tools.
Detection accuracy: Evaluate the solution's ability to identify relevant threats.
Reliability: Test updates, restarts, and unexpected system conditions.
Scalability: Determine how performance changes as deployment expands.
Documenting these results helps teams identify weaknesses before releasing the product.
Monitor Performance After Deployment
Pre-release testing cannot represent every real-world environment. Continuous monitoring helps vendors identify performance degradation, compatibility problems, and emerging security risks.
Useful indicators include application latency, resource consumption, alert frequency, update failures, and security incident trends. Regular updates, controlled deployments, and rollback procedures can help reduce operational risks.
Feedback from customers and technical support teams can also reveal issues that require further investigation.
How OEM Integration Supports Scalable Software Products
OEM integration enables software vendors to incorporate security capabilities into products distributed under their own brands or as part of broader technology offerings.
A suitable integration approach can help maintain consistent security controls across supported environments while reducing the need to develop every capability independently. However, vendors must consider product architecture, licensing, technical support, and long-term maintenance.
They should also clarify responsibilities for vulnerability management, security updates, and compatibility testing. These measures help ensure that integrated security capabilities remain effective as products and customer requirements evolve.
Connecting Endpoint Security With Broader IT Security
Endpoint protection is an important security layer, but it cannot address every threat independently. Organizations also need controls that protect network traffic, manage access, and monitor connected systems.
A cloud network security service can complement endpoint protection through capabilities such as traffic monitoring, access restrictions, and network security policy enforcement.
For example, endpoint controls may identify suspicious activity on a device, while network controls can help restrict unauthorized communications. Coordinating these measures can improve visibility and support a more comprehensive security response.
Organizations should also consider multifactor authentication, least-privilege access, and centralized logging. The appropriate combination depends on infrastructure, business risks, and compliance requirements.
Applying Security Principles to Education Software
Education platforms process sensitive information, including student records, attendance details, and staff information. Protecting these resources requires security measures across applications and the devices used to access them.
A school management web app builder can support the development of education platforms tailored to institutional workflows. Security requirements should be considered alongside usability, accessibility, and performance.
Important safeguards include:
Role-based access: Restrict records according to each user's responsibilities.
Strong authentication: Reduce the risk of unauthorized account access.
Data encryption: Protect sensitive information during transmission and storage.
Secure updates: Address known vulnerabilities in applications and supported devices.
Endpoint protection: Help secure staff devices used to access institutional systems.
Together, these measures can reduce security risks while supporting reliable education management operations.
Best Practices for Choosing an OEM Endpoint Security Integration Approach
Selecting an integration approach requires an understanding of both technical and business requirements. Vendors should evaluate the following factors before making a decision:
Compatibility: Confirm support for required operating systems, hardware, and software architectures.
Performance benchmarks: Review measurable results for resource consumption and application responsiveness.
Threat detection: Assess whether the solution addresses relevant security risks.
Integration documentation: Evaluate APIs, configuration options, and deployment guidance.
Maintenance: Clarify responsibilities for patches, updates, and vulnerability management.
Scalability: Understand how licensing and technical requirements change as deployment grows.
Technical support: Check the availability of assistance and product updates.
A pilot deployment can help validate these requirements before a wider release. Testing in a representative environment provides practical evidence of how the solution performs under expected workloads.
Balance robust threat protection with reliable application performance. Contact us today to discuss your OEM endpoint security integration requirements.
Conclusion
Balancing performance and protection in OEM endpoint security integrations requires careful architecture, efficient resource management, compatibility testing, and continuous monitoring.
Software vendors should evaluate security effectiveness and application responsiveness together throughout development and deployment. Combining endpoint protection with appropriate network controls, identity safeguards, and secure development practices can further strengthen overall security.
A well-planned integration strategy helps OEMs build reliable, scalable products while protecting users and maintaining the performance they expect.
Frequently Asked Questions
1. What is an OEM endpoint security integration solution?
It enables OEMs and software vendors to incorporate endpoint security capabilities into their products. Depending on the implementation, these capabilities may include malware detection, threat prevention, behavioral monitoring, and security management.
2. How can endpoint security affect application performance?
Security processes may consume CPU, memory, and network resources. Poorly optimized scanning and monitoring can slow applications. Efficient configuration and performance testing help minimize these effects.
3. What should OEMs test before integrating endpoint protection?
They should assess compatibility, resource consumption, detection accuracy, application stability, update behavior, and scalability across representative environments.
4. Can endpoint security work with cloud network security?
Yes. Endpoint security protects individual devices, while network security controls help manage communications and access. Together, they provide complementary layers of protection.
5. Why is continuous monitoring important after integration?
Monitoring helps vendors identify performance issues, compatibility problems, excessive alerts, and emerging threats. Regular updates and testing help maintain protection as products evolve.