Buying a dark web monitoring platform is the easy part. The harder part is turning it into a service that clients understand, analysts can run without burning out and your finance team can price with confidence. Plenty of providers switch a tool on, watch alerts pile up and quietly stop looking at them within a quarter.
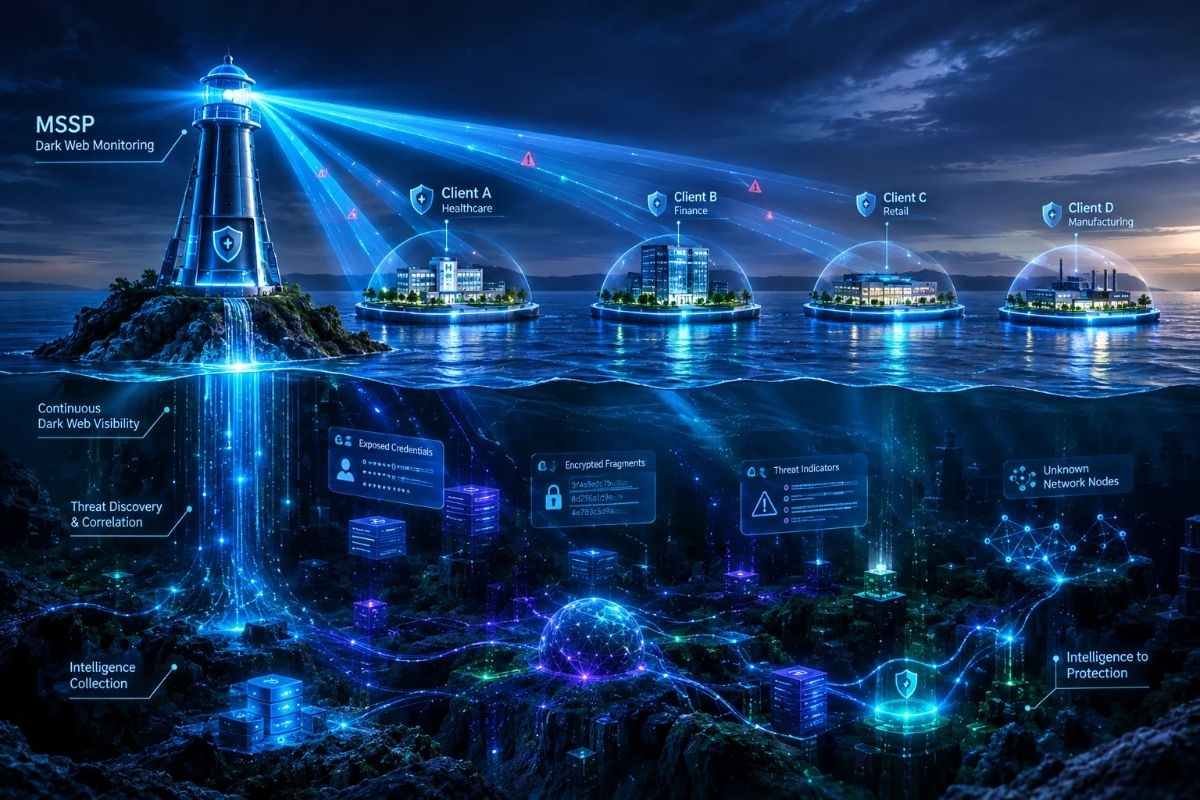
MSSP dark web monitoring works when it is treated as a delivery process, not a feed. Someone owns onboarding, someone triages, someone talks to the client and someone reports on outcomes. This guide covers that operating model from start to finish: how to onboard a client, how to triage alerts by severity, how to package service tiers, what to report, which numbers to track and where delivery usually breaks. If you are still choosing tooling, a purpose-built MSSP dark web monitoring platform is worth reviewing alongside the process advice below, because the two decisions affect each other.
What Does It Mean to Run MSSP Dark Web Monitoring as a Service?
Running MSSP dark web monitoring as a service means defining who monitors which client assets, how findings are triaged, how clients are notified and how results are reported over time. The tool collects and matches data. The service is the set of people, playbooks and promises wrapped around it. Clients pay for the outcome, which is fewer exposed credentials turning into incidents.
A working service has five parts:
Scope: the domains, executives, brands and vendors covered for each client.
Detection: the platform that watches criminal sources and matches findings to that scope.
Triage: a repeatable way to decide what matters and what does not.
Response: clear actions that reduce risk after a finding, owned by named people.
Reporting: proof to the client that the work is happening and getting results.
Most failed launches skip one of these. The most common gap is response, where the provider tells the client about an exposure and then leaves the client to work out what to do.
Where It Fits in a Managed Security Stack
Dark web monitoring sits next to MDR, endpoint protection, email security and identity controls. It contributes an outside-in view: what has already leaked, before it shows up as a login attempt on your client's systems. Position it that way. It does not replace detection tools inside the network and saying it does invites disappointment.
Why Providers Add Dark Web Monitoring to Their Offering
Providers add it because it addresses a real and common attack path, it is easy for clients to understand and it supports both new sales and renewals. Exposed credentials are a routine ingredient in account takeover and ransomware intrusions and monitoring gives you something concrete to show clients between incidents.
It Answers a Question Clients Already Ask
Clients regularly ask some version of "are our passwords out there?" A monitoring service gives you a direct, evidence-based answer instead of a general reassurance. That turns a vague worry into a defined deliverable.
It Strengthens Retention
Security work is hard to notice when it succeeds. A monthly report showing exposures found, actions taken and repeat exposures falling gives clients a reason to keep paying. It also gives your account managers something specific to discuss during reviews.
It Opens Doors With Prospects
A light exposure summary for a prospect's domain often starts a better conversation than a slide deck. Many providers offer it as a low-friction first step, then propose a managed service once the prospect sees real findings. If your platform supports prospecting workflows, this can become a repeatable pipeline motion rather than a one-off favor.
The Threat Data Supports the Case
Industry reporting backs up the concern. According to Verizon's 2026 Data Breach Investigations Report, ransomware appeared in 48 percent of the breaches it analyzed and third-party involvement in breaches rose 60 percent year over year. Both trends put pressure on providers to know what is exposed across a client and the vendors around it. Verify figures against the latest edition before quoting them to clients, since report numbers change each year.
How to Onboard a Client Onto Dark Web Monitoring
Onboarding a client means collecting the assets to monitor, confirming ownership, setting alert routing and running a baseline scan. A clean onboarding takes a short time and prevents most later confusion. Skipping it produces a noisy first week that teaches the client to ignore your alerts.
Step 1, Define the Scope
Ask the client which primary domains, subsidiary domains and brand names to include. Add executive and finance-team addresses if the service tier covers VIP monitoring. Also ask about acquired companies and legacy domains, since forgotten domains are a frequent source of unexpected exposure.
Step 2, Confirm Domain Ownership
Verify that the client controls each domain before monitoring begins. This protects you and the client and it prevents someone from adding a domain they do not own. Record who approved the scope and when.
Step 3, Run a Baseline Scan
The first scan will surface historical exposures accumulated over the years. Treat this as a one-time cleanup, not a fire drill. Separate old, low-risk findings from fresh ones and present the baseline to the client as a starting point with a plan attached.
Step 4, Set Alert Routing
Decide who receives what. Your analysts should see everything. The client's IT contact might get a summary or only high-severity items. Executive exposures may need a discreet path to a named person. Configure these routes before the first live alert, so the first real finding lands in the right place.
Step 5, Explain What Alerts Mean
Give the client a one-page explainer covering alert types, what you will do on their behalf and what you need them to do. Clients who understand the process respond faster and complain less about noise.
Step 6, Agree on Response Ownership
Write down who resets passwords, who reviews sign-in logs, who confirms multi-factor authentication is on and who signs off on closing a finding. Ambiguity here is the single biggest cause of stalled alerts.
Alert Triage Playbooks by Severity
Alert triage sorts findings from your MSSP dark web monitoring platform into severity tiers, each with a defined response and timeline. A simple three-tier model works for most providers: high for fresh, usable credentials or session data, medium for recent but less certain exposures and low for old or duplicate records. Clear tiers keep analysts fast and consistent.
High Severity
High-severity findings include recent infostealer log entries with a plaintext password, session cookies tied to a corporate application, or credentials for privileged accounts. The response should start the same day. Typical steps are forcing a password reset, invalidating active sessions, checking recent sign-in activity for the account and confirming multi-factor authentication. If the source suggests the device is infected, involve the client's endpoint team, because changing the password alone does not remove the malware.
Medium Severity
Medium findings are recent exposures that lack clear proof of active use, such as a corporate email appearing in a fresh third-party breach with a hashed password. The response is usually a prompt password reset if the credential may be reused, plus a reminder to the user about password reuse. These can be handled within a normal working window.
Low Severity
Low findings are old breach records, duplicates of exposures already handled and data with little context. Log them, add them to the periodic report and do not page anyone. The goal is to record them without creating alert fatigue.
Escalation Rules
Define when a finding jumps a tier. A credential belonging to an administrator, a finance approver, or an account with access to sensitive systems should move up regardless of source. Repeated exposure of the same account should also trigger a conversation, since it points to a habit or a compromised device rather than a one-time leak.
Closing a Finding
A finding is closed when the action is done and recorded, not when the alert is read. Record what was exposed, what you did, who confirmed it and the date. This record becomes the evidence you show in reports, audits and renewal conversations.
Packaging Dark Web Monitoring Into Service Tiers
Most providers package the service in tiers based on scope and response depth: a basic tier with automated alerts, a standard tier with analyst triage and monthly reporting and an advanced tier with executive monitoring, faster response commitments and integration with the client's own tools. Tiers let you serve different budgets without building custom scopes every time.
A sensible structure looks like this:
Basic: domain-level monitoring, automated alerts and a periodic summary. Best for small clients who want coverage without much interaction.
Standard: everything in Basic, plus analyst review of high and medium findings, guided remediation steps and a monthly report.
Advanced: everything in Standard, plus executive and brand monitoring, vendor or subsidiary coverage, defined response times and integrations with the client's ticketing or SIEM tools.
I am not listing prices, because the right figures depend on your costs, your market and your platform's pricing model. Build them from your own numbers. Include the cost of analyst time in your model, since triage labor is usually the largest hidden cost.
Keep the Promise Small and Specific
Write service descriptions in terms you can deliver. Promise monitoring of defined sources, alerting within a stated window and guided remediation. Avoid promising to find every leak or to prevent every breach. Specific, modest commitments are easier to meet and easier to defend.
White-Label Considerations
If you resell under your own brand, confirm that the platform lets you brand the dashboard, alerts and reports. It matters more than it sounds. When clients see your name on every touchpoint, monitoring becomes part of your offering instead of a visible third-party tool and your relationship with the client stays intact.
Reporting, What Clients Want to See
Good monitoring reports show what was found, what was done and how exposure is trending. They should be short, consistent and written for a business reader. A report that lists every historical leak buries the message. A report that tells a clear story of action and progress earns renewals.
A useful monthly report includes:
A summary of new exposures by severity.
Actions taken on each high and medium finding, with dates.
Open items that need the client's attention.
Trend lines, such as repeat exposures and time to remediate.
Recommendations, such as enforcing multi-factor authentication or retiring an old domain.
Keep a quarterly version for executive readers that focuses on trend and risk, not individual records. Also protect sensitive details. Do not paste plaintext passwords into reports. Reference the account and the source and store the raw data securely.
Measuring the Service, KPIs That Matter
The best KPIs measure response and repeat risk, not raw alert counts. A high alert count says little on its own. What matters is how quickly your team acts and whether the same problems keep coming back. Track a handful of numbers consistently and review them monthly.
Time to triage: how long a high-severity finding waits before an analyst reviews it.
Time to remediate: how long until the credential is reset, sessions are revoked and the finding is closed.
Repeat exposure rate: the share of findings tied to accounts that were exposed before.
Coverage: the share of client domains and priority accounts under active monitoring.
MFA coverage on exposed accounts: whether the affected users are protected by a second factor.
Client engagement: how quickly clients respond to items that need their input.
Why these numbers? IBM's 2026 Cost of a Data Breach Report puts the average breach cost at 4.99 million dollars and the average time to identify and contain a breach at 247 days. Providers cannot control those averages, but they show why speed and early detection carry weight in client conversations. As with any report figure, confirm it against the current edition before publishing it in client materials.
Comparing Service Delivery Models
Providers usually run dark web monitoring in one of three ways: fully automated alerting, analyst-led managed service, or a hybrid. The right choice depends on client size, analyst capacity and how much guidance clients expect. Each model trades cost against depth.
Delivery Model | Who Triages Alerts | Client Effort | Analyst Load | Best Fit |
Automated alerting only | The client or their IT contact | High, the client interprets and acts | Very low | Small clients with a capable internal IT contact |
Analyst-led managed service | Your analysts | Low, you guide remediation | High, scales with client count | Clients who want a fully managed outcome |
Hybrid with automation and analyst review | Automation filters, analysts handle high severity | Medium | Moderate | Providers balancing margin and service quality |
Automated-only delivery is cheap and scales, but it pushes interpretation onto clients who may not have the skills. Fully analyst-led delivery gives clients the best experience and is the most expensive to staff. Most providers land on the hybrid model, where the platform deduplicates and scores findings, analysts step in for high and medium severity and low-severity items roll into periodic reports.
Staffing and Workflow Considerations
Dark web monitoring does not need a dedicated team at small scale, but it needs a clear owner. One or two analysts can typically handle triage alongside other duties if the platform filters well. As client count grows, alert volume and reporting effort rise and the work needs scheduled time on someone's calendar.
Fit It Into Existing Workflows
Route alerts into the tools your team already uses. If your analysts live in a ticketing or PSA system, findings should become tickets automatically. If you run a SIEM or SOAR platform, look at whether dark web findings can enrich other detections. Manual copying between systems is a reliable way to lose findings.
Use Role-Based Access Sensibly
In a multi-tenant environment, define who can see which clients. Analysts may need broad access, while account managers and client users should see only their own data. Role-based access control protects client confidentiality and reduces risk if credentials on your side are ever exposed.
Train for Judgment, Not Just Process
Playbooks handle common cases, but analysts need judgment for edge cases. Is this a fresh infostealer entry or a recycled record? Does this account have privileged access? Regular review of closed findings helps analysts calibrate and helps you improve the playbooks.
Common Delivery Failures and How to Avoid Them
Most delivery problems come from unclear ownership, poor tuning and weak follow-through, not from the technology. Knowing the usual failure points lets you design around them before they show up in a client escalation.
Alerts with no owner. If nobody is assigned to a finding, nobody acts on it. Give every alert an owner and a due date.
Starting with a data dump. Sending a client a huge list of historical exposures on day one overwhelms them. Summarize the baseline and give a plan.
No repeat-exposure review. The same accounts keep appearing because the underlying cause, such as password reuse or an infected device, was never addressed. Review repeats and fix the cause.
Reports that only count alerts. Counts without actions look like activity, not value. Show what you did and what changed.
Ignoring session and infostealer data. Password resets alone do not help when an attacker holds a valid session token. Revoke sessions and check the device.
Overstating coverage. Do not claim to watch the entire dark web. State which source types you cover and where visibility ends.
Treating monitoring as standalone. Pair it with multi-factor authentication, password manager adoption and endpoint protection so alerts lead to lasting improvement.
Interesting Facts About Dark Web Monitoring Operations
These facts come from published reports and public sources. Figures change with each edition, so check the latest versions before citing them.
Verizon's 2026 Data Breach Investigations Report found ransomware present in 48 percent of the breaches it analyzed, which is one reason credential exposure is treated as an early warning sign.
The same Verizon report noted that third-party involvement in breaches rose 60 percent year over year, which supports monitoring vendors and subsidiaries where the service tier allows it.
IBM's 2026 Cost of a Data Breach Report puts the average breach cost at 4.99 million dollars and the average time to identify and contain a breach at 247 days.
Security research firms track infostealer malware as its own threat category, since it collects saved passwords, cookies and session tokens that criminals then trade in log form.
Have I Been Pwned, maintained by security researcher Troy Hunt, indexes data from publicly known breaches. It is a useful reference for historical exposure but does not provide continuous monitoring of underground sources.
Industry groups and analysts continue to describe credential-based attacks, including credential stuffing and account takeover, as a persistent pattern across sectors and annual breach reports update their rankings each year.
Conclusion
MSSP dark web monitoring succeeds or fails on delivery. The platform finds exposures, but the service is what turns them into reduced risk and renewed contracts.Start small and specific. Define scope with each client, write playbooks for the three severity levels, pick a delivery model that matches your staffing and measure time to remediate and repeat exposure. Be honest about what monitoring can and cannot see and pair it with multi-factor authentication and strong password practices. If you want to see how a white-label, multi-tenant option supports this operating model, take a look at what Mispar offers for MSSPs.
Frequently Asked Questions (FAQs)
How do MSSPs deliver dark web monitoring to clients?
MSSPs deliver dark web monitoring by defining each client's domains and priority accounts, running continuous monitoring through a multi-tenant platform, triaging alerts by severity and guiding remediation. They then report on findings and outcomes on a regular schedule. The service combines a tool with playbooks, named owners and client communication.
How long does it take to onboard a client onto dark web monitoring?
Onboarding is typically quick, because the main tasks are confirming domains, setting alert routing and running a baseline scan. The time depends on how many domains the client has and how fast they approve scope. Allow extra time to explain alert types and agree on who handles remediation.
What should an MSSP dark web monitoring report include?
A strong report includes new exposures by severity, actions taken with dates, open items that need client input and trends such as repeat exposures and time to remediate. Add short recommendations, such as enforcing multi-factor authentication. Avoid printing plaintext passwords and keep executive summaries brief.
Should MSSPs use automated alerts or analyst-led triage?
Most providers use a hybrid. Automation deduplicates and scores findings and analysts review high and medium severity items and guide remediation. Fully automated delivery is cheaper but leaves interpretation to the client, while fully analyst-led delivery gives the best experience but costs more to staff.
How should an MSSP price dark web monitoring?
Price it based on your own costs, your platform's pricing model and the depth of service in each tier. Include analyst triage time in the calculation, since labor is often the largest hidden cost. Tiering by scope and response depth lets you serve different client budgets without custom quotes.
What metrics show that dark web monitoring is working?
Useful metrics include time to triage, time to remediate, repeat exposure rate, coverage of client domains and MFA coverage on exposed accounts. These show whether your team acts quickly and whether the same issues keep returning. Raw alert counts alone say little about service quality.